FinTech Security: Building Zero-Trust Architecture for Open Banking APIs
01 Oct 2026
Open
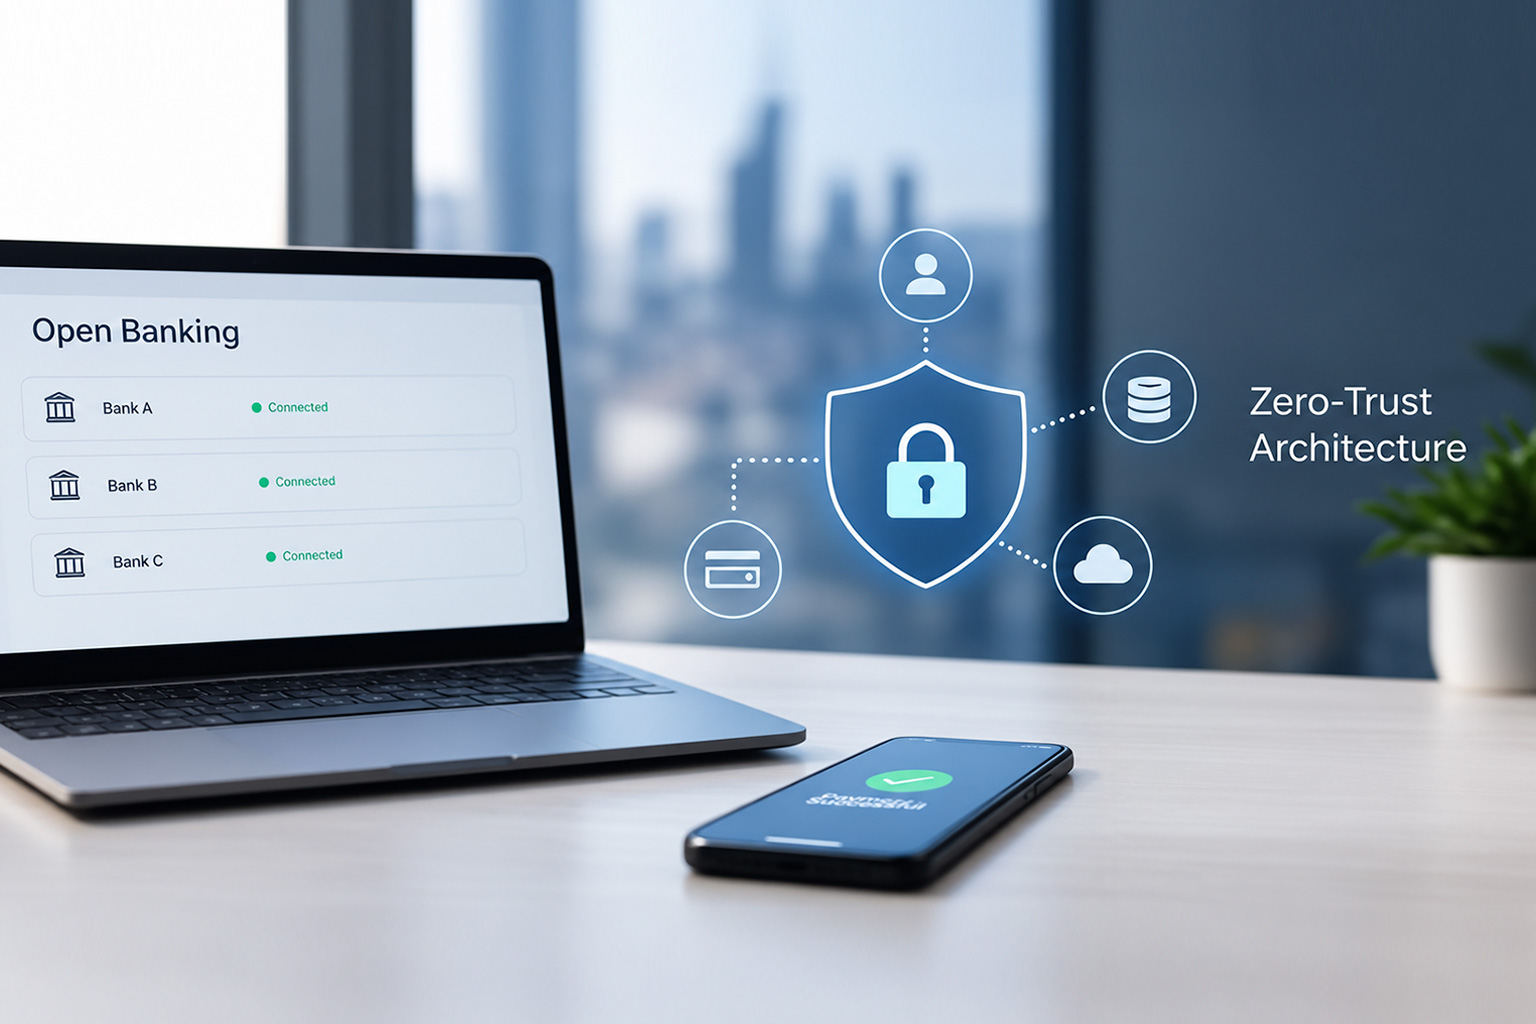
banking has transformed the financial technology sector, enabling third-party
providers to connect directly with banking systems and deliver innovative
financial services. However, exposing core banking services via APIs introduces
unique security challenges. Simply placing an API behind a traditional network
perimeter or a basic firewall is no longer sufficient.
Modern financial applications rely on third-party providers, sensitive
consumer financial data, API credentials, access tokens, and distributed cloud
systems. When authorization models fail, or tokens are intercepted, attackers
can gain direct access to core banking engines. Securing open banking
ecosystems requires shifting away from implicit trust models toward a
Zero-Trust architecture designed specifically for financial APIs..
Quick Summary: What Is Zero-Trust Security in Open Banking APIs?
Zero-Trust security in open
banking is an operational framework operating on the principle of "never
trust, always verify." It replaces network-perimeter assumptions with
explicit identity
verification, least-privilege authorization, continuous monitoring, and
workload authentication via mTLS and OAuth 2.0.
Why Traditional API Security Is Not Enough for FinTech
Legacy security strategies were designed around a trusted corporate network protected by perimeter firewalls. In an open banking environment, that boundary no longer exists. APIs are exposed to the public internet to serve mobile apps, web clients, and third-party partners.
Relying exclusively on traditional defenses creates critical vulnerabilities:
- Firewalls
and VPCs: Perimeter controls assume that traffic originating inside the network
is safe, leaving internal microservices vulnerable if a single component is compromised. - IP allowlists and API keys: Static API keys can be easily leaked or extracted from client-side code, while dynamic cloud scaling renders IP allowlisting ineffective.
- Compromised credentials and stolen tokens: If an attacker intercepts a standard bearer token, they can impersonate a legitimate user or third-party provider until the token expires.
- Excessive internal privileges: Giving internal services broad access to databases or upstream systems allows lateral movement if an attacker breaches one service layer.
Traditional API Security vs. Zero-Trust Architecture
|
Security Area |
Traditional Approach |
Zero-Trust Approach |
|
Trust |
Network-based trust |
Explicit identity verification |
|
Authentication |
API keys/basic authentication |
Strong client/workload authentication |
|
Authorization |
Broad permissions |
Least-privilege policies |
|
Internal services |
Trusted network |
Authenticated service-to-service access |
|
Monitoring |
Periodic review |
Continuous monitoring and logging |
The 4 Key Pillars of Zero-Trust Open Banking Security
1. OAuth 2.0 and FAPI
OAuth 2.0 provides the foundational framework for delegated authorization, allowing users to grant third-party applications limited access to their financial data without sharing passwords. For financial services, the OpenID Foundation developed Financial-grade API (FAPI) profiles. FAPI builds stricter security and cryptographic requirements on top of OAuth 2.0 and OpenID Connect, addressing token leakage, authorization code interception, and secure data exchange.
2. mTLS and Service Identity
Mutual Transport Layer Security (mTLS) ensures that both the client and the server authenticate each other using digital certificates during the TLS handshake. In financial API environments, mTLS secures service-to-service communication and binds access tokens to the client's cryptographic certificate, preventing token replay attacks.
3. Fine-Grained Authorization
Authentication verifies who is making a request, but authorization determines what they are allowed to do. Zero-Trust architectures enforce least-privilege access using Role-Based Access Control (RBAC) or Attribute-Based Access Control (ABAC). Financial APIs must validate transaction scopes, user consent, and resource-level permissions before fulfilling any data request.
4. Key and Secret Protection
Cryptographic keys, client secrets, and transport certificates form the backbone of API security. Organizations must implement strict certificate lifecycles, automated key rotation, and secure storage mechanisms. While Hardware Security Modules (HSMs) help protect sensitive cryptographic materials, they must be paired with disciplined operational governance.
mTLS vs. OAuth 2.0: What's the Difference?
A common point of confusion in API security is distinguishing between transport security and token-based authorization:
· mTLS (Mutual Transport Layer Security): Operates at the transport layer, verifying communicating parties through digital certificates and encrypting the communication channel.
· OAuth 2.0: Operates at the application layer, providing a framework for delegated authorization and issuing scoped access tokens.
They are not competing alternatives. A highly secure financial API implements both: mTLS authenticates the workload and secures the transport tunnel, while OAuth 2.0 validates user consent and authorizes specific data access actions.
A Practical Zero-Trust Architecture for Open Banking APIs
A resilient open banking request flows through distinct security validation layers:
Client / TPP -> Authentication -> API Gateway -> Authorization -> Application Services -> Financial Data
Core security controls are distributed across this pipeline:
- API Gateway: Enforces rate limiting, input validation, and initial TLS termination.
- mTLS & FAPI Validation: Confirms client workload identity and verifies cryptographic token binding.
- Authorization Engine: Evaluates fine-grained scopes, user consent, and policy rules.
- Secrets Management & Logging: Protects backend credentials while maintaining continuous audit trails.
Common FinTech API Security Mistakes
- Trusting internal network traffic: Assuming that traffic inside a private cloud cluster is inherently secure.
- Treating mTLS as complete authorization: Believing that a valid client certificate grants blanket access to all endpoints.
- Giving services excessive permissions: Assigning overly broad database or API scopes to microservices.
- Using long-lived credentials: Failing to enforce short token expiration windows and automated rotation.
- Poor key/certificate management: Allowing expired certificates or mismanaged private keys to disrupt service or invite compromise.
- Logging sensitive financial information: Inadvertently writing Personally Identifiable Information (PII) or tokens into log files.
- Assuming an API gateway solves every security problem: Relying on edge proxies without implementing application-level controls and workload verification.
How to Implement Zero Trust for Open Banking APIs in 2026
- Map data and workflows: Catalog all APIs, third-party integrations, data flows, and sensitive financial endpoints.
- Establish strong identities: Implement robust cryptographic machine identities for services and secure user authentication.
- Deploy FAPI and mTLS: Adopt FAPI-compliant OAuth flows and enforce mutual TLS for confidential clients.
- Enforce least-privilege policies: Restrict API access using precise scopes, consent checks, and attribute-based rules.
- Monitor and refine: Continuously log API traffic, analyze anomaly patterns, and update security controls.
How NanoByte Technologies Can Help
NanoByte Technologies delivers enterprise software development and cybersecurity solutions tailored for complex digital environments. With core capabilities spanning cloud architecture, API development, DevOps, and cybersecurity services, NanoByte helps financial technology organizations engineer secure, scalable backend systems. Partner with NanoByte Technologies to strengthen your software infrastructure.
Partner with NanoByte Technologies.
FAQs
What is Zero Trust API security in FinTech?
Zero Trust API security is an operational model based on strict verification. It eliminates implicit trust based on network location, requiring continuous authentication, strict authorization checks, and encrypted workload communications for every API request.
What is the difference between mTLS and OAuth 2.0?
mTLS is a transport-layer protocol that uses digital certificates to mutually authenticate communicating parties and encrypt the connection. OAuth 2.0 is an application-layer authorization framework that issues tokens granting delegated access to resources.
Is mTLS required for Open Banking APIs?
Yes, modern open banking security profiles, such as FAPI specifications, strongly mandate mTLS for client authentication and token binding to prevent interception and impersonation risks.
Does Zero Trust replace an API gateway?
No. An API gateway remains a vital component for traffic management, rate limiting, and initial request routing, working alongside Zero Trust policies to protect backend services.
Does Zero Trust guarantee regulatory compliance?
No single architecture or technology guarantees regulatory compliance. Zero Trust provides technical safeguards, but compliance requires ongoing legal, operational, and procedural alignment with applicable regulations.
How can FinTech companies protect API credentials?
FinTech organizations protect credentials by utilizing secure hardware modules, automating key and certificate rotation, avoiding hardcoded secrets, and enforcing strict least-privilege access policies across all services.
.jpg)