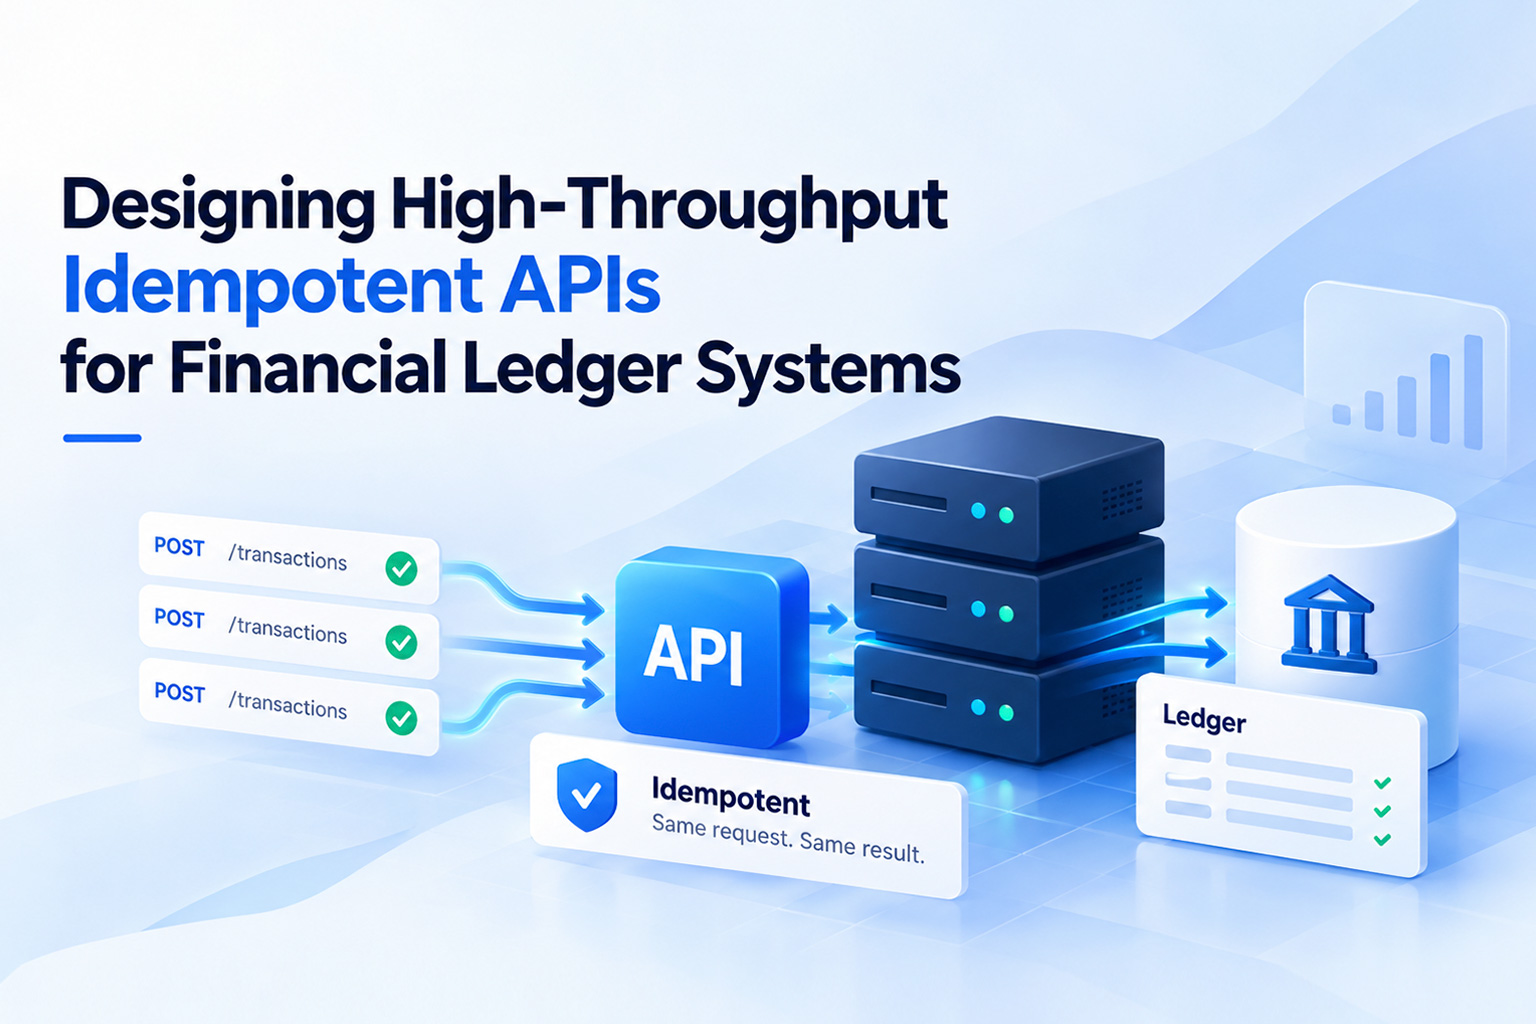
Designing High-Throughput Idempotent APIs for Financial Ledger Systems
20 Oct 2026
Introduction: When a Network Retry Becomes a Financial Risk
A client submits a payment request. The server validates it, posts the ledger entries, and commits, but the connection drops before the response arrives. The client times out and retries. Without safeguards, the second request creates a second financial operation, and one customer intent becomes two debits.
Timeouts, retry logic, concurrent requests, and partial failures make this scenario routine in distributed systems. Idempotent API architecture for fintech platforms addresses it by letting the system recognize a retry as the same logical operation. But idempotency is one part of a broader financial integrity strategy. An idempotency key alone does not guarantee correct balances, prevent every duplicate payment, or replace database transactions and reconciliation. If you are researching how to build idempotent APIs for financial ledgers in 2026, this article shows how the pieces fit together.
Quick Summary: What Is Idempotency in Financial Ledger APIs?
Idempotency means repeated submissions of one logical operation return a consistent outcome while its financial effect is applied only once within a defined scope. That guarantee holds only when key handling, durable state, transaction boundaries, and recovery logic are all implemented correctly.
1. Why Financial APIs Need Protection Against Retries and Race Conditions
Network timeouts and retry storms. A request can succeed on the server even though the client never sees the response. Aggressive retries, especially from many clients at once, multiply the effect. A retry must return the original result rather than create a second payment or ledger posting.
Concurrent requests. Two requests can arrive with the same idempotency key at nearly the same moment. If the code first checks whether the key exists and then inserts a record in a separate, unprotected step, both requests can pass the check before either writes. Claiming the key has to be a single atomic operation.
Partial failures. A database commit, an external payment-provider call, and the response to the client do not succeed or fail together. A timeout on a provider call does not prove the call failed. Systems need an explicit uncertain state and a way to resolve it, instead of treating every timeout as a failure.
Idempotency does not prevent all double-spending or incorrect balances. Authorization, balance checks, concurrency control, transaction integrity, and reconciliation are still required.
2. Standard REST APIs vs. a Robust Idempotent Financial API
REST is not inherently unsafe. RFC 9110 defines PUT, DELETE, and the safe methods as idempotent, but POST carries no such guarantee, and payment APIs often use it to create a payment or submit a transaction. Those operations need application-level safeguards.
|
Area |
API without idempotency controls |
Robust idempotent API design |
|
Request retries |
Each retry may create a new operation |
A retry of the same logical operation returns the stored outcome |
|
Duplicate-key handling |
No key, or a key checked without durable state |
Scoped key stored durably with a request fingerprint |
|
Concurrent requests |
Check-then-insert races can admit duplicates |
Atomic claim through a unique constraint or equivalent |
|
Transaction and ledger integrity |
Postings may be partial or unlinked |
Balanced entries committed atomically with the operation record |
|
Failure recovery |
Timeouts leave unknown state |
Persisted status supports safe resolution and reconciliation |
|
Auditability and reconciliation |
Hard to tie requests to postings |
Each posting traces to a key, request, and external reference |
The core of a robust idempotent API design is a stable idempotency key that represents one logical operation, paired with a durable record of that operation’s status and outcome. Retrying means resending the same key. Intentionally creating a new payment means generating a new one. Stripe documents one provider-specific implementation of this model; it is a useful example, not a universal standard.
3. Four Technical Pillars of a High-Throughput Idempotent Architecture
Pillar 1: Idempotency Keys and Durable Request State
In Stripe-style idempotency key design, the client generates a unique key per logical operation and reuses it on every retry. The server scopes the key to a defined context, such as merchant, account, endpoint, or transaction type, so identical strings from different tenants never collide. A robust record typically includes:
- A unique constraint on the scoped key, or equivalent atomic coordination, so only one request can claim it.
- A request fingerprint and an operation status, such as in progress, succeeded, or failed.
- The stored outcome, returned when an eligible duplicate arrives.
- Defined behavior for duplicates that arrive while the original is still processing, such as a conflict or retry-later response.
Retention and expiration should reflect business risk, provider contracts, and client retry behavior, not a fixed default. Redis can provide low-latency coordination or caching, but it should not be the only source of truth for critical financial operations unless its durability and recovery guarantees have been explicitly established. The durable database record and transaction design usually matter more than cache speed.
Pillar 2: Concurrency Control and Atomic Processing
When two requests with the same key arrive together, exactly one must win the claim. A dependable approach is an atomic insert-or-claim against a uniqueness constraint in the primary database; the losing request reads the existing record and responds according to its status. PostgreSQL documents both unique constraints and its MVCC model, including row-level locking, so critical state transitions can run inside transactions rather than depend on application-side checks.
Redis-based distributed locks are one possible coordination technique, not a universal requirement, and Redlock is not mandatory. Locks alone do not guarantee financial correctness, because lock expiration, process crashes, network partitions, and retries can leave two workers believing they hold the same lock. Where practical, use the database’s transactional guarantees to protect state transitions. For balance-affecting operations, validation and posting should be atomic, so two concurrent debits cannot both pass the same balance check.
Pillar 3: Double-Entry Ledger Integrity
In double-entry bookkeeping, a balanced transaction records corresponding debit and credit entries according to the ledger’s accounting model. Useful practices include:
- Append-only or immutable posting records where appropriate, with corrections made through new reversing entries.
- Atomic posting of every entry belonging to one transaction.
- Explicit transaction states and references linking entries to the originating operation and key.
Balances can be derived from ledger entries or maintained as materialized projections. Deriving them maximizes auditability but can cost read performance; cached balances speed reads but add a second structure that must stay consistent and be reconciled. Neither approach is universally correct. Reconciliation against external payment-provider or bank records catches what in-flight controls miss. Idempotency prevents repeated application of a logical operation; ledger rules and transaction controls preserve accounting consistency.
Pillar 4: Request Fingerprints, Replay Handling, and Recovery
The server should bind each key to the original request’s relevant parameters through a stored fingerprint. If the same key arrives with a materially different payload, the API should reject the conflicting reuse rather than silently apply a different operation. A 409 Conflict may be appropriate, but status codes should follow the API’s documented contract. Fingerprints must be calculated consistently over the fields that define the operation; hashing raw JSON without canonicalization breaks on field ordering, omitted defaults, and semantically equivalent payloads.
For requests stuck in progress or with an uncertain outcome, recovery should rely on persisted operation state, transaction boundaries, and reconciliation, not on blindly repeating external payment effects. Querying a provider with a stored external reference is safer than resubmitting. A transactional outbox or durable event record helps coordinate database changes with downstream messages and improves reliable delivery, but it does not make every external side effect exactly-once.
4. Frequently Asked Questions
How long should idempotency keys be stored in a financial ledger system?
There is no universal 24- or 72-hour standard. Retention depends on the operation, client retry policy, provider requirements, dispute and reconciliation needs, and the cost of a late duplicate. Short-term response caches can expire sooner, while durable transaction records often persist much longer.
What happens if a client sends the same idempotency key with a modified payload?
A robust API compares the request against the fingerprint stored with the original key and rejects the conflicting reuse according to its documented error contract, often a 409 Conflict or similar client error. It should never apply the new payload under the old key.
Does an idempotency key guarantee that a payment can never be duplicated?
No. Keys prevent repeated application of one logical operation only when key scope, durable state, concurrency handling, external-provider coordination, and reconciliation are also correct. A client generating a fresh key for the same intent can still create duplicates.
How can a financial API handle a timeout after a payment request?
The client should retry with the same key or query the existing operation’s status, not generate a new payment request. The server must safely resolve whether the original operation succeeded, failed, or remains uncertain, using persisted state and provider status checks.
How do you design idempotent APIs for high throughput?
Use indexed key lookups, atomic uniqueness enforcement, short critical sections, and carefully selected caching that never replaces durable state. Add observability for conflicts and lock waits, and load test realistically. Performance depends on your actual workload and consistency requirements.
Building Reliable Financial APIs with NanoByte Technologies
Robust financial API development goes well beyond a key lookup. It can involve idempotency design, payment workflow modeling, transactional database architecture, concurrency control, ledger integrity, observability, failure recovery, and performance benchmarking.
Whether you are evaluating a financial ledger software development company, looking for custom payment ledger API developers, or planning to hire fintech backend architects for a high-throughput platform, the right starting point is your own failure modes, provider contracts, and throughput targets, not a generic template.
Building or scaling payment APIs and financial ledger systems? Partner with NanoByte Technologies to design reliable transaction workflows, strengthen data integrity, and benchmark backend performance against your business requirements.
.jfif)
.png)